
Your Biggest Compliance Risk Is the One You Don’t See Coming
Most therapists assume they are compliant until an audit proves otherwise.
HIPAA compliance is not based on what you believe you are doing correctly. It is based on what you can produce, document, and defend when asked.
Without written HIPAA policies, a completed Security Risk Analysis, and your state’s requirements clearly documented, you are already out of compliance and would likely fail an audit.
The Security Risk Analysis is the foundation of the HIPAA Security Rule and one of the most common enforcement findings cited by the Office for Civil Rights (OCR).
Does using an EHR make me HIPAA compliant?
No.
An EHR is a tool, not proof of compliance.
HIPAA requires documented policies, a completed Security Risk Analysis, and ongoing risk management regardless of what software you use. Many fined providers had EHR systems but no documented risk analysis.
HIPAA Security Risk Analysis & Compliance Monitoring Systems
A Security Risk Analysis is not just another HIPAA checklist. It requires you to look at how your practice handles electronic client information, identify where vulnerabilities exist, evaluate the risks, and document what you’re doing to address them.
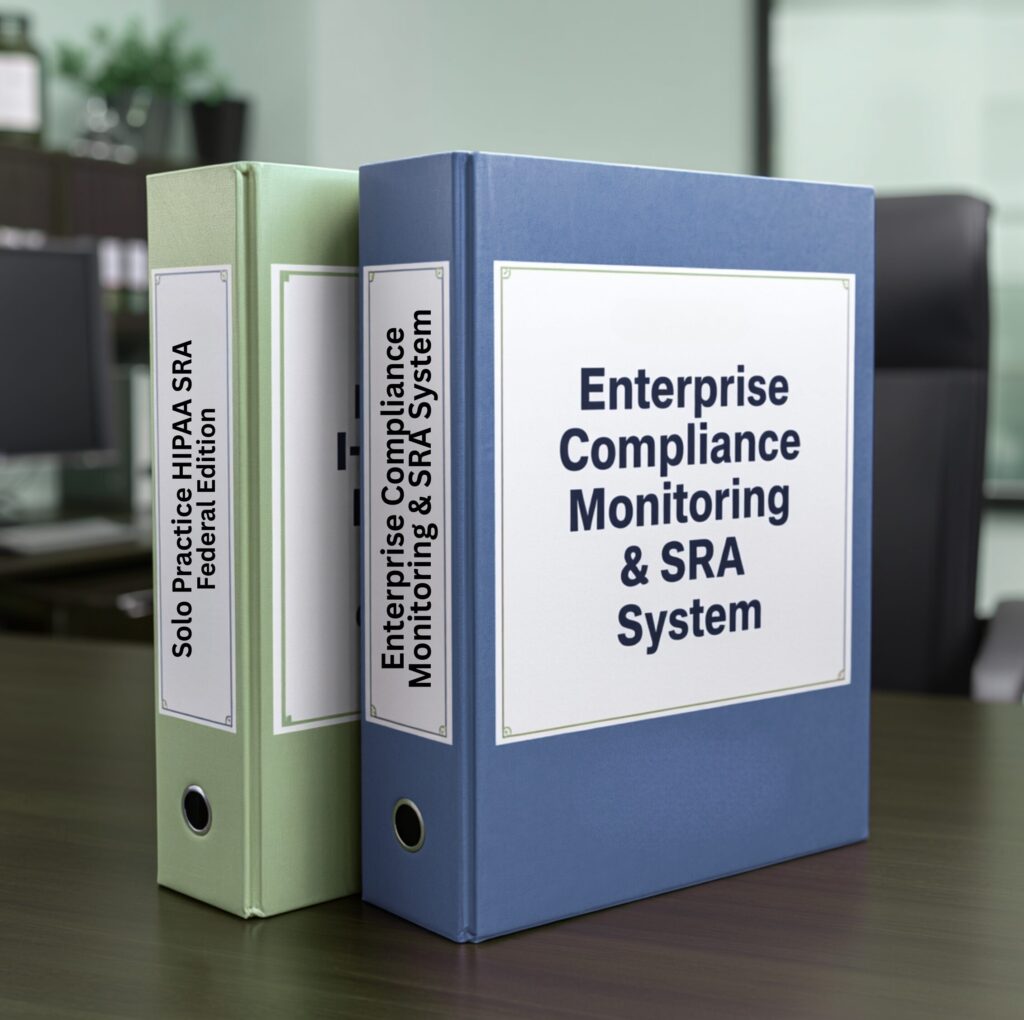
Guardian Clinical Essentials offers two structured systems designed specifically for behavioral health practices: one for independent solo providers and another for group practices with more complex systems, staffing, and oversight responsibilities.
Both are designed to help you conduct and document your Security Risk Analysis and maintain the records needed for ongoing risk management.
The Compliance Gap You Did Not Know You Had
Federal HIPAA enforcement actions repeatedly identify some of the same problems:
Using an EHR does not mean your practice is HIPAA compliant.
Having HIPAA policies does not replace conducting a Security Risk Analysis.
Many practices have never documented how they evaluate risks to electronic client information.
As practices grow, additional staff, vendors, systems, and workflows create more opportunities for security vulnerabilities.
And here’s where therapists can get into trouble. You may have security measures in place, but if you haven’t evaluated your risks and documented what you’re doing to address them, you’re missing an important part of HIPAA compliance.
A Security Risk Analysis helps you identify those gaps before a breach, complaint, or investigation forces you to look for them.
Without these in writing, you risk:
Having no proof of compliance during an audit
Missing critical requirements you were never taught
Fines, ethics complaints, or board action against your license
And this is not rare. Licensing boards, insurance panels, and federal auditors request these documents every single year.
When you cannot produce them, you are already out of compliance, even if no breach has occurred.
Here’s what I wish more therapists realized:
the Security Risk Analysis isn’t optional, and having an EHR, a HIPAA manual, or a signed BAA doesn’t mean you’ve met this requirement.
And OCR isn’t just going after hospitals and large healthcare systems. Behavioral health practices have been cited and fined for failing to conduct an adequate Security Risk Analysis.
If you’re wondering what HIPAA requires, what counts as an SRA, or whether you’ve been doing enough, I break it all down here:
HIPAA Security Risk Analysis for Therapists: What’s Required, What Counts, and Where to Start
This Isn't Just a HIPAA Technicality. Practices Are Being Fined for Missing SRAs.
These are real enforcement actions from the U.S. Department of Health and Human Services Office for Civil Rights (OCR). Every single one involved failing to complete a proper Security Risk Analysis (SRA) and the penalties were severe.
Deer Oaks Behavioral Health
📄 The Trigger: Ransomware attack in August 2023 exposed PHI for more than 171,000 individuals.
⚠️ The Finding: OCR found Deer Oaks had not conducted an accurate and thorough risk analysis as required by HIPAA.
💸 The Outcome: $225,000 settlement and a two-year corrective action plan requiring a compliant SRA and ongoing monitoring. (HHS OCR, July 7, 2025)
Anchorage Community Mental Health Services
📄 The Trigger: Malware infection exposed ePHI for 2,743 individuals.
⚠️ The Finding: OCR determined the provider had not conducted a thorough risk assessment and was running outdated, unpatched software.
💸 The Outcome: $150,000 settlement plus a corrective action plan mandating a complete SRA and security updates. (HHS OCR, December 2014)
Metro Community Provider Network (Denver)
📄 The Trigger: Phishing attack compromised ePHI for 3,200 individuals.
⚠️ The Finding: OCR concluded the provider failed to perform a comprehensive risk analysis and lacked a formal risk management process.
💸 The Outcome: $400,000 settlement and a multi-year corrective action plan, including a complete SRA. (HHS OCR, April 12, 2017)
Is a Security Risk Analysis Required by Law
or Just Recommended?
Required.
HIPAA mandates an accurate and thorough risk analysis for any practice handling electronic protected health information. This is a legal requirement under the HIPAA Security Rule, not a best practice.
Required under 45 CFR §164.308(a)(1)(ii)(A)
What You’ll Get
You shouldn’t have to piece together an SRA from random checklists, generic templates, and information that doesn’t account for how behavioral health practices operate.
Both systems provide a structured way to evaluate your practice’s security risks, document your findings, and track what needs attention.
Identify Risks You May Be Missing
Look at the systems, devices, vendors, and everyday workflows that create, receive, maintain, or transmit electronic client information.
Evaluate Your Existing Safeguards
Document the protections you already have in place, identify vulnerabilities, and evaluate risks based on likelihood and impact.
Document Your Security Risk Analysis
Organize your findings and supporting documentation so you have a record of the assessment you’ve conducted, rather than relying on assumptions about your compliance.
Create a Plan to Address Identified Risks
Prioritize corrective actions, document what needs to happen, and track your progress toward addressing vulnerabilities.
Support Ongoing Risk Management
Use the included logs and tracking tools to document reviews, monitor security concerns, and update your risk management activities as your practice changes.
Yes - The Security Risk Assessment Is Mandatory
HIPAA requires:
“An accurate and thorough assessment of the potential risks and vulnerabilities to the confidentiality, integrity, and availability of electronic protected health information.”
– HIPAA 45 CFR §164.308(a)(1)(ii)(A)
Both systems are designed to help you conduct and document the Security Risk Analysis required under federal HIPAA regulations. They walk you through evaluating your practice’s actual systems, identifying risks and vulnerabilities, documenting existing safeguards, and developing a plan to address the concerns you identify.
The difference is in the complexity of your practice. Solo providers and group practices have different systems, workflows, and responsibilities, which is why we offer two versions.
Who This System Is For
Solo therapists operating independently without staff or contractors accessing client information
Group practice owners managing multiple clinicians, staff, or contractors
Clinical supervisors, practice administrators, and compliance officers responsible for security oversight
Behavioral health practices using EHRs, telehealth platforms, electronic communication, and other systems that handle client information
Practices expanding their services, adding providers, or preparing for regulatory reviews
Designed for Ongoing Use
Use your SRA system:
At least annually: As a recommended practice standard to review your risks, safeguards, and any changes that may affect the security of client information.
When your practice changes: Adding providers, staff, technology, vendors, services, or new workflows can introduce risks that weren’t part of your previous assessment.
When new risks or security concerns arise: Reevaluate affected systems and document any corrective actions needed.
When preparing for an audit or compliance review: Make sure your assessment, risk management activities, and supporting documentation accurately reflect how your practice operates.
Choose the Compliance System
That Fits Your Practice
You do not need to figure this out on your own. Choose the version that matches your practice structure and level of complexity.
Solo Practice System
Solo Practice HIPAA Security Risk Analysis – Federal Edition
A comprehensive, editable Security Risk Analysis system developed specifically for independent mental health providers. It walks you through evaluating your practice’s actual technology, workflows, vulnerabilities, and safeguards, with documentation tools to support ongoing risk management.
Includes:
- Federal HIPAA Security Risk Analysis framework
- Asset inventory and PHI flow mapping
- Threat, vulnerability, likelihood, and impact evaluation
- Administrative, technical, and physical safeguard reviews
- Corrective action planning and verification
- System activity, technical evaluation, and vendor/BAA tracking logs
Best for:
- Independent solo therapists
- Practices without staff, contractors, or other individuals accessing PHI
- Providers who need a structured, therapist-specific approach to documenting their SRA
Value: $3,250
Regular Price: $1,997
Limited-Time Price: $997
“I didn’t realize how much
I didn’t know.”
Enterprise / Group Practice System
Enterprise HIPAA Compliance Monitoring & Security Risk Analysis System
A comprehensive Security Risk Analysis and ongoing monitoring system designed for behavioral health group practices. It addresses the additional risks and responsibilities that come with multiple providers, workforce access, vendors, shared systems, and more complex practice operations.
Includes:
- Enterprise-level Security Risk Analysis framework
- Risk evaluation and corrective action planning
- Administrative, technical, and physical safeguard reviews
- Workforce access, oversight, and security documentation
- Vendor risk and Business Associate Agreement tracking
- Ongoing compliance monitoring and review logs
- Documentation tools to support risk management and regulatory reviews
Best for:
- Group and multi-provider practices
- Practices with employees, contractors, interns, or billing personnel
- Multi-location practices
- Practice owners and compliance personnel managing more complex security responsibilities
Value: $9,800
Regular Price: $2,497
Limited-Time Price: $1,497
“This likely saved me thousands of dollars in potential fines.”
Operating in More Than One State?
Our Enterprise SRA + Monitoring System includes state-specific compliance considerations based on your practice’s location.
If your practice operates in multiple states, additional requirements may apply. Contact us to discuss your practice’s needs and multistate pricing.
Licensing & Terms
One license covers one purchasing practice or business entity.
Enterprise state-specific customization includes one state. Additional states require a separate quote.
Documents are editable for the purchasing practice’s internal use.
Sharing, redistribution, or resale is prohibited.
Future regulatory updates are not included unless separately purchased or provided.
Format & Delivery
📥 Delivered within 5-8 business days
🖊️ Customized with your business name + watermark
🔐 Internal-use license (one business)
🖊️ Fully editable + customizable
📅 Reusable and customizable as your practice evolves, with periodic review and updates needed to reflect changes in regulations, technology, and operations.
Updates & Ongoing Maintenance
The purchasing practice is responsible for reviewing and updating its Security Risk Analysis as regulations, technology, staffing, and operations change. Future updates are not automatically included with purchase.
If you need assistance determining what changes are necessary, Guardian Clinical Essentials offers consultation services. Depending on the scope of the changes, you may only need targeted updates rather than an entirely new SRA system.
Security Risk Analysis Questions
Therapists Ask Most
Do therapists actually have to complete a Security Risk Analysis?
Yes.
HIPAA requires every covered entity to conduct an accurate and thorough assessment of risks to electronic protected health information. This is a federal requirement, not a best practice.
How often does a Security Risk Analysis need to be completed?
Best practice is annually or whenever practice changes occur.
There is no fixed annual requirement in HIPAA law. A Security Risk Analysis must be completed initially and updated whenever your practice changes or new risks emerge. Most compliance experts recommend reviewing it at least annually as a best practice.
What happens if I have never completed an SRA?
You are already out of compliance.
Failure to complete a Security Risk Assessment is one of the most common findings in federal enforcement actions. If a breach, complaint, or audit occurs, you may face penalties and be required to complete one under a corrective action plan.
Is a Security Risk Analysis only required for large practices or hospitals?
No.
The HIPAA Security Rule applies to covered entities and business associates regardless of size. That includes solo therapists and small behavioral health practices when they meet the definition of a HIPAA covered entity.
Being a one-person practice doesn’t exempt you from conducting a Security Risk Analysis.
What exactly does a Security Risk Analysis evaluate?
It evaluates how your practice protects client information.
This includes devices, email, telehealth platforms, EHR systems, staff access, storage methods, and breach readiness. The goal is to identify vulnerabilities and document how you are addressing them.
Is this the same as a HIPAA checklist or training?
No.
A checklist or training does not replace a risk assessment.
HIPAA requires written analysis of risks and documented risk management steps. Education alone does not satisfy the Security Rule requirement.
Will completing an SRA prevent an audit?
No.
But not having one guarantees problems if you are audited.
A completed and maintained Security Risk Assessment demonstrates active compliance. Without it, you cannot show regulators or licensing boards that required safeguards are in place.
Does this include state laws or only federal HIPAA?
It depends on the system you choose.
The Solo Practice SRA System is designed to meet federal HIPAA requirements.
The Enterprise Compliance Monitoring & SRA System includes both federal HIPAA and state-specific mental health compliance requirements.
What kinds of penalties happen when SRAs are missing?
Financial settlements and corrective action plans are common.
Federal enforcement actions frequently cite failure to complete a Security Risk Assessment. Penalties may include fines, required monitoring, and multi-year compliance oversight.
Is an SRA a one-time document or something I maintain?
It must be maintained and updated.
HIPAA expects practices to review and update their risk analysis regularly. Each update should reflect current technology, staffing, and services.
Who should be responsible for completing the SRA in a practice?
Practice leadership is responsible.
Owners, compliance officers, or designated privacy and security leads typically oversee the process. Even in solo practices, responsibility cannot be delegated away.
What should happen after the Security Risk Analysis is completed?
Risk management and ongoing monitoring must follow.
HIPAA expects practices to address identified risks, update policies, and document corrective actions. A structured monitoring system helps ensure compliance stays current as your practice evolves.
What is the difference between a Security Risk Assessment and a Security Risk Analysis?
They are often used interchangeably. Under HIPAA, the requirement is an “accurate and thorough risk analysis” identifying vulnerabilities to ePHI, followed by risk management actions.
What law requires a Security Risk Analysis?
HIPAA Security Rule – 45 CFR §164.308(a)(1)(ii)(A)